AI Voice Assistant
Ask about open incidents, risks and audits by voice or text. Answers come from your live data.
Secure · Comply · Govern
SAHS unifies governance, risk, audit and compliance — with an AI internal auditor — so teams move from fragmented controls to continuous assurance across ISO 27001, SOC 2, GDPR, DPDPA, PCI DSS and 40+ frameworks.
Our solutions · select to preview
Our solutions
Platform capabilities
Services
Frameworks
Ask about open incidents, risks and audits by voice or text. Answers come from your live data.
Aria interviews your team like a human auditor, says what is right or wrong and how to fix your documents.
ISO 27001, 9001, 22301, 20000, 27701, 45001, 14001, GDPR, DPDPA, NIST, SOC and CSCRF.
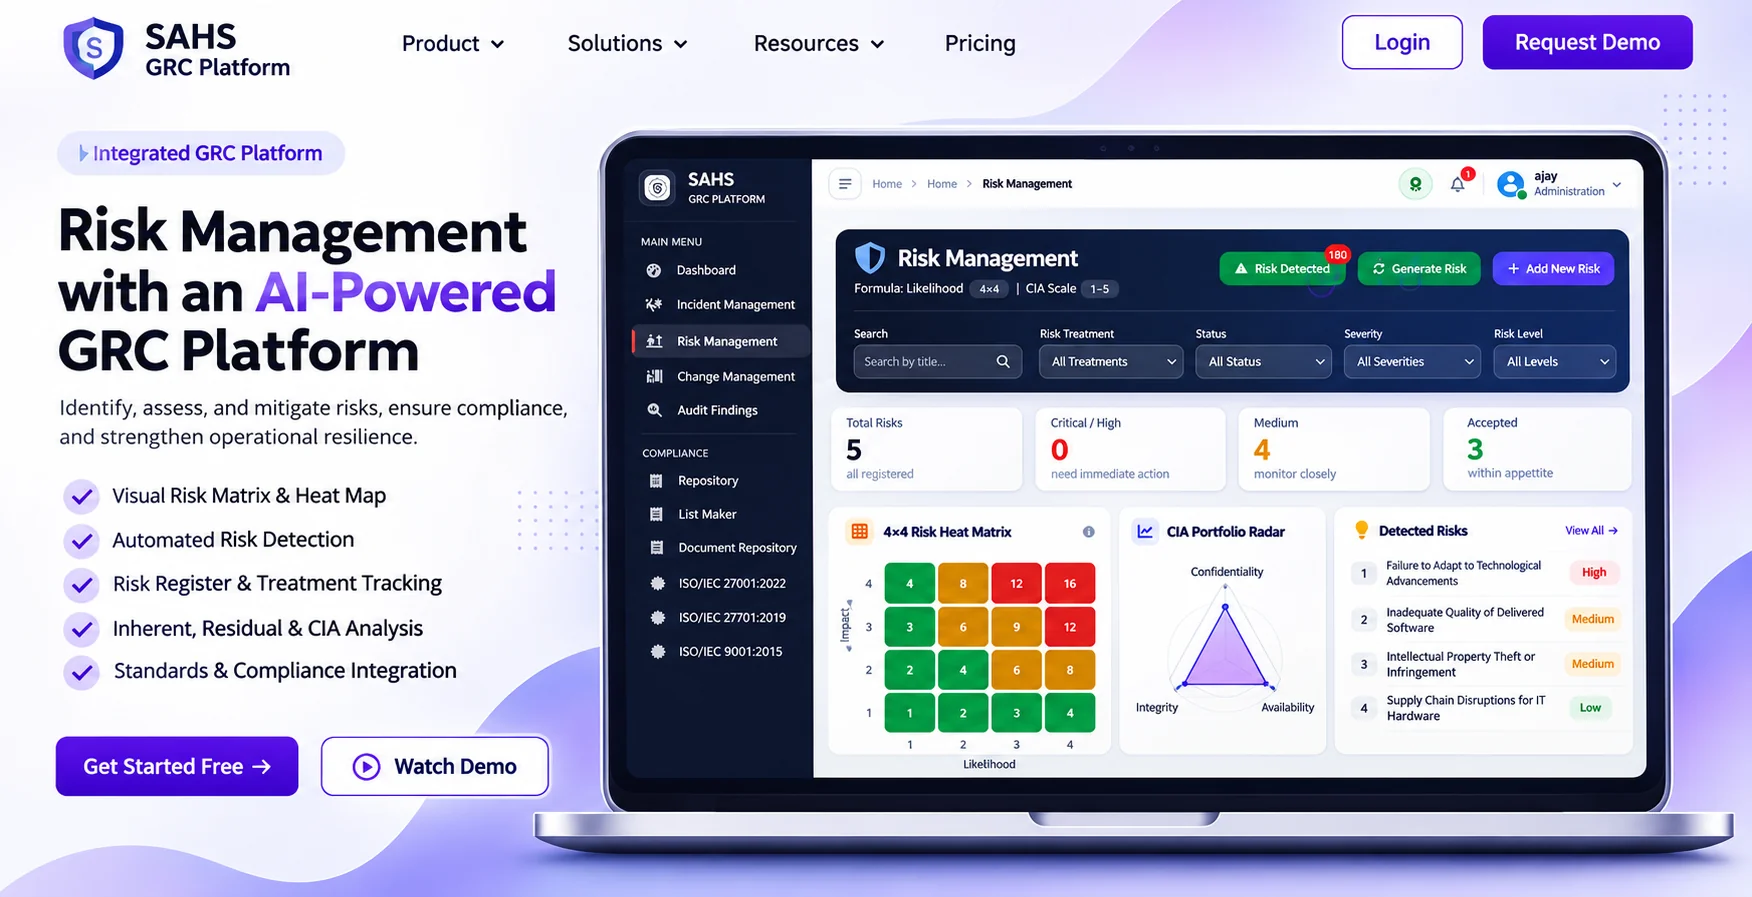
Log, assign and close incidents, risks, non-conformances and CAPA with full history.
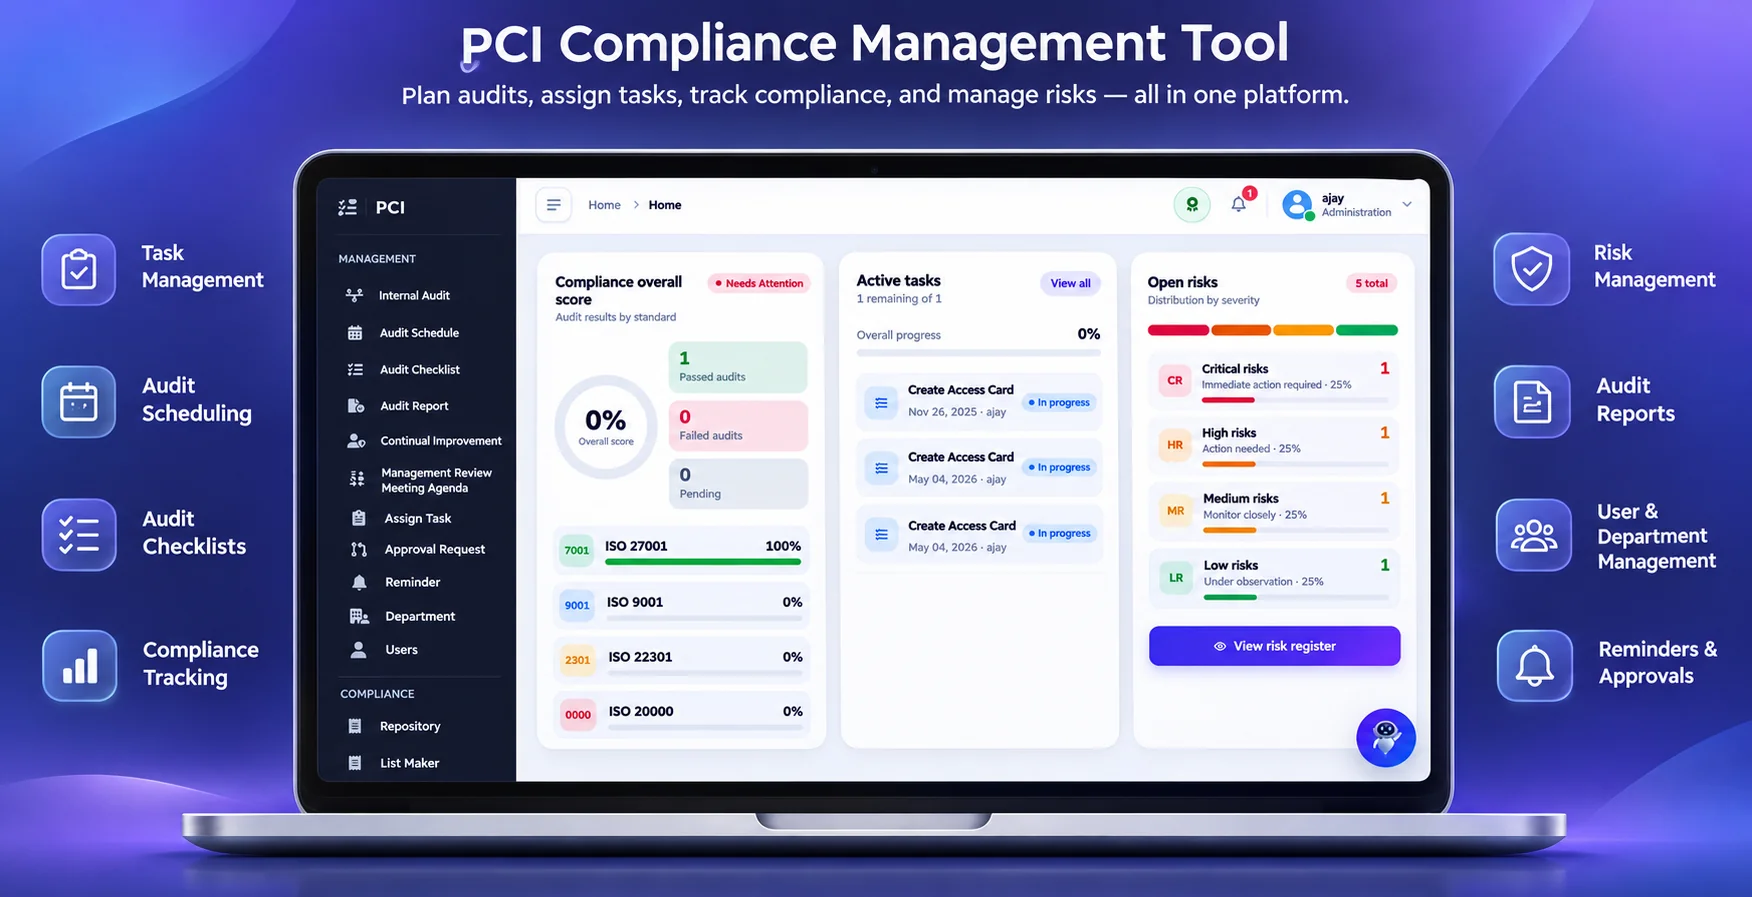
Plans, schedules, checklists and reports for internal audits and management review.
Clauses, controls, policy templates and evidence in one place for certification audits.
Pick ISO, GDPR, DPDPA, NIST or SOC and load the matching clauses, controls and policies.
Record risks, incidents and non-conformances, assign owners and close corrective actions.
Run an AI-led internal audit by voice, then download a report with improvements.
Interactive 3D loads only when you click, so the page stays fast.
3D model "Security Cyborg" by fletcherkinnear, CC BY, via Sketchfab.
GRC stands for Governance, Risk and Compliance: the way an organisation sets policies, manages risks and proves it meets standards such as ISO 27001, GDPR and NIST.
SAHS is a GRC platform where teams manage policies, controls, risks, incidents, non-conformances, corrective actions, internal audits and certification evidence in one system.
SAHS covers ISO 27001, 9001, 22301, 20000, 27701, 45001 and 14001, plus GDPR, DPDPA, NIST, SOC and SEBI CSCRF checklists.
Yes. The built-in AI assistant answers questions from your live compliance data, opens forms and pages, and supports voice. An AI internal audit agent interviews users by voice and suggests document improvements.
Yes. It provides clauses, Annex A controls, policy templates, audit planning, checklists and reports that support ISO 27001 certification readiness.
Use the Request Demo button on this page or register at /register.php, and the team will contact you.
Our clients
Regulatory coverage
Pricing
Start with the essentials, add AI assurance and frameworks as you grow. No hidden fees.
Prices per month, excluding applicable taxes. Need more users, on-premise or custom frameworks?
Compare plans
FAQ
See how SAHS can transform the way you manage cybersecurity, risk and compliance.
Walk through the platform with a specialist and see it applied to your environment.
Book a Demo →Plan implementation, integrations and a governance programme built around your regulations.
Contact sales
Get a personalised demo, a tailored quote or help choosing a plan. We map SAHS to your frameworks in under 30 minutes.
What happens next
* Required. We never share your details.
Explore what SAHS covers: governance, risk and compliance software, ISO 27001, SOC 2, GDPR, DPDPA, internal audit, vendor risk and more.